Every policy in one place, approved, current and acknowledged.

Write each policy or bring the one you have, route it for approval, send it to the people it covers, and keep it current on a review schedule. The record builds itself as you go.

30-day trialUnlimited free viewersNo credit card required

From first draft to the audit, in five steps

One job, start to finish. Each step links to the part of the product that does it.

  1. 01

    Write it, or bring it

    Draft privately until it is ready, or upload the PDF you already have. On a yearly plan, we move your documents in for you.

    Versions and Reviews
  2. 02

    Approve it

    Route it through up to four steps, with anyone in the company as an approver. It is locked while in review, and reminders keep it moving.

    Approval Workflows
  3. 03

    Send it to the people it covers

    Tags decide who receives it. Choose notify or acknowledge when you send it, and new hires get theirs on day one.

    Policy Distribution and Access
  4. 04

    Keep it current

    Review dates remind each policy’s editor. If nothing changed, the date moves; if it changed, the new version goes through approval and out again.

    Versions and Reviews
  5. 05

    Prove it, or publish it

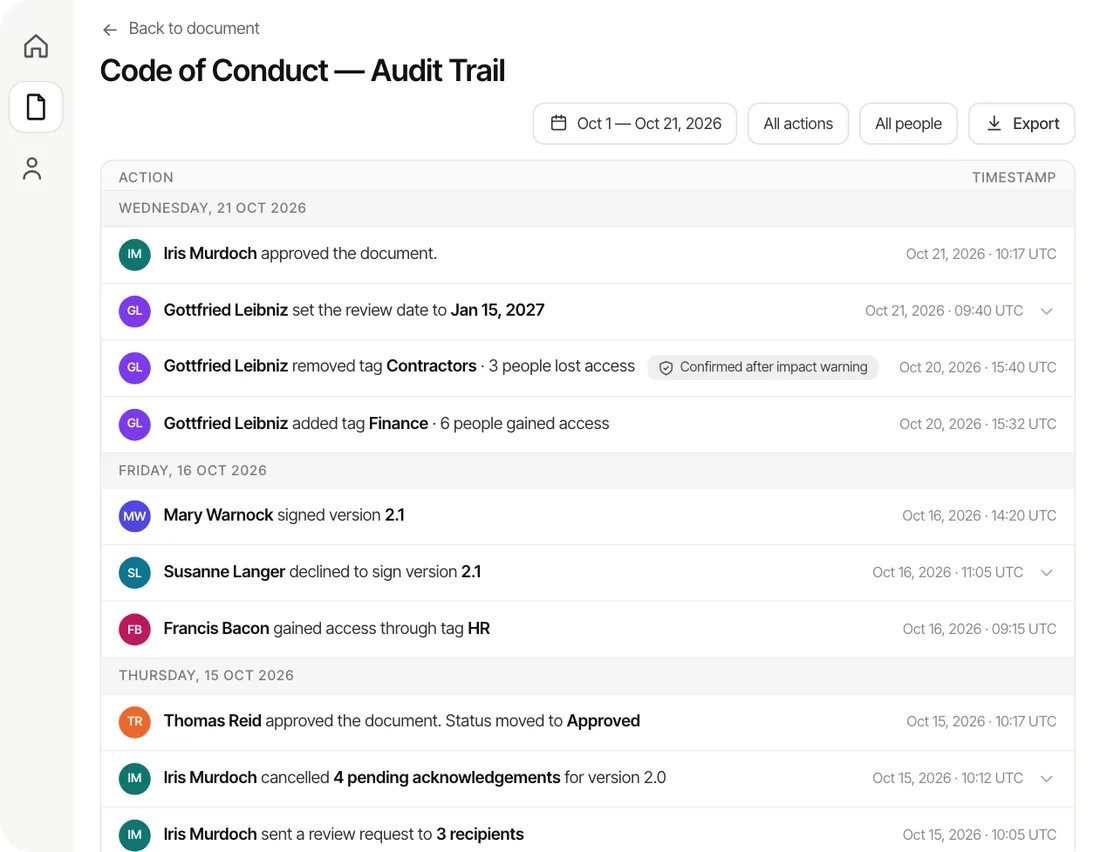
    Filter the record and export a PDF or CSV. Publish chosen policies on your site, from the same approved version.

    Audit Trail and Export

One current version

Every change becomes a new version. Compare any two and see what changed, word by word.

Reviews that keep it current

Review dates remind the editor. If nothing changed, the date moves and nobody is asked again.

Who asks to see it

Inside the company and outside it, people ask the same question: is the policy approved, current and known to the people it covers.

Inside the company

  • Leadership and the boardWhich policies are current, and who approved each one.
  • Department headsThe current version of the policies their team follows.
  • LegalWhat changed between two versions, and who approved the change.
  • Internal auditApprovals and review dates across the whole set.

Outside it

ISO 9001, clause 7.5

Documented information

Documents approved before use, changes controlled, and the current version available where it is used, with obsolete versions kept out of circulation.

  • Approval before use, on record
  • One current version for everyone
  • Earlier versions kept in history

ISO/IEC 27001, clause 5.2, control A.5.1

Policies for information security

Policies approved by management, communicated, acknowledged by the people they cover and reviewed at planned intervals.

  • Approvals by the people you choose
  • Acknowledged by each person it covers
  • Planned reviews on review dates

SOC 2, Trust Services Criteria CC5.3

Policies and procedures

Control activities are put in place through policies that say what is expected and procedures that put them into action.

  • Policies and procedures held together
  • Each one approved and versioned
  • The record ready for the audit window

Wherever you operate

Local laws

Each country and state adds its own written policies, from harassment and leave to safety and privacy. Each gets its place beside the rest.

  • A policy for each country or state
  • Sent only to the people it applies to
  • Each change goes out again

Bring your own rules

Your region’s laws, the standards your customers ask for, and your own house rules. Write each one as a policy, approve it, and send it to the people it covers.

  • Laws of every country and state you work in
  • Standards and certifications
  • Customer and contract requirements
  • Your own policies and procedures
Check what your laws requirePolicy and Compliance lists the documents a business has to have in writing, by country and business type.Check your laws (opens in a new tab)

For every policy the company runs on

Whichever department writes it, every policy follows the same cycle.

  • Employee handbook
  • Code of conduct
  • Information security policy
  • Data protection policy
  • Health and safety policy
  • Quality policy
  • Travel and expense policy
  • Delegation of authority
  • Anti-bribery policy
  • Remote work policy

Who can do what

EditorsWrite policies, send them for approval and acknowledgment, and set review dates.
ApproversAnyone in the workspace who can see the policy, including viewers. No seat needed.
ViewersRead the policies that cover them and acknowledge them. Free, however many you have.
AdminsManage people and tags, and see the workspace log.

Need help writing the policies? Find a consultant for your standard.

Questions

Can we bring the policies we already have?

Yes. Upload a policy as a PDF and send it for acknowledgment, or draft it in AllyMatter. On a yearly plan, we move your documents in for you.

Who can approve a policy?

Anyone in the workspace who can see it, including viewers. Up to four steps, with up to six people in each.

What happens when I update a policy?

It becomes a new version and goes through approval. Everyone keeps seeing the current version until the new one is approved, then everyone it covers is asked again.

What happens at a review if nothing changed?

The editor moves the review date. There is no new approval and nobody is asked again.

Can the same policy be public?

Yes. Publish an approved policy as a public page, on your own domain on the Scale plan.

Can I see who has not acknowledged?

Yes. You can see at a glance who has acknowledged and who has not, and reminders go out until they do.

Try AllyMatter free for 30 days

  • No credit card needed
  • 30-day money-back guarantee
  • Free migration on yearly plans