Every security policy approved, acknowledged and ready for the audit.
For IT and security teams who own the information security policy and everything under it. Each policy approved, sent to the people it covers, and on record by person and by version.
Information Security PolicyVersion 5.3Owned by IT & Security
Drafted
Security team
Gilbert Ryle, Head of security
Annual review: a new AI use section, tighter access rules
1 Oct 2026
Step 1 · Technology
Alfred Whitehead
Chief technology officer
Approved3 Oct 2026
Step 2 · Leadership
Simone de Beauvoir
Chief executive
Approved6 Oct 2026
Sent to everyone
All staff, 164 people
163 of 164
acknowledged version 5.3
The policies you own
The security policy is the top of a set. Each policy under it reaches a different group, on its own review cycle.
Information security policy
The policy everything else hangs from, and the first document any auditor or customer asks for.
Acceptable use
Everyone acknowledges it, and it is where consent to monitoring of company systems is set out.
Access control
Who gets what, who approves it, and how access is removed when people change roles or leave.
Incident response
The plan your on-call team follows, current before the day it is needed.
Secure development and change
How code and infrastructure change safely, for the engineers who make the changes.
AI use
Which tools are approved and what data goes into them, current as the tools change.
Who asks to see them
Wherever you operate, auditors, customers and regulators ask the same question: is the policy approved, current and known to the people it covers.
ISO/IEC 27001, clauses 5.2, 7.3, A.5.1
Information security policies
The policy and the topic policies under it are approved by management, communicated, acknowledged by the people they cover and reviewed at planned intervals.
Every policy approved and versioned
Acknowledged by each person it covers
Planned reviews on review dates
PCI DSS v4.0, Requirement 12
Security policy and awareness
The security policy is reviewed at least once a year, and personnel confirm at least once a year that they have read and understood it.
A yearly expiry date that brings it back for approval
Everyone asked again once it is re-approved
Each acknowledgment by person and version
GDPR, Articles 24 and 39
Data protection policies
Controllers put appropriate data protection policies in place, and staff who handle personal data are made aware of them.
Data protection policies approved and versioned
Sent to the teams that handle personal data
Awareness on record by person and version
Wherever you hold data
Local privacy and security laws
Breach notice, privacy and sector rules differ by country and by state. Each one gets its own addendum beside the core security policy.
An addendum for each country or state
Sent only to the people it applies to
Each change goes out again
Bring your own rules
Your region’s laws, the standards your customers ask for, and your own house rules. Write each one as a policy, approve it, and send it to the people it covers.
Invite someone with their tags and their policies are waiting.
No seat cost for readers
Employees and other viewers are unlimited and free. You pay for the people who write.
Yearly cycles on schedule
Review and expiry dates remind each policy’s owner ahead of time.
Proof on request
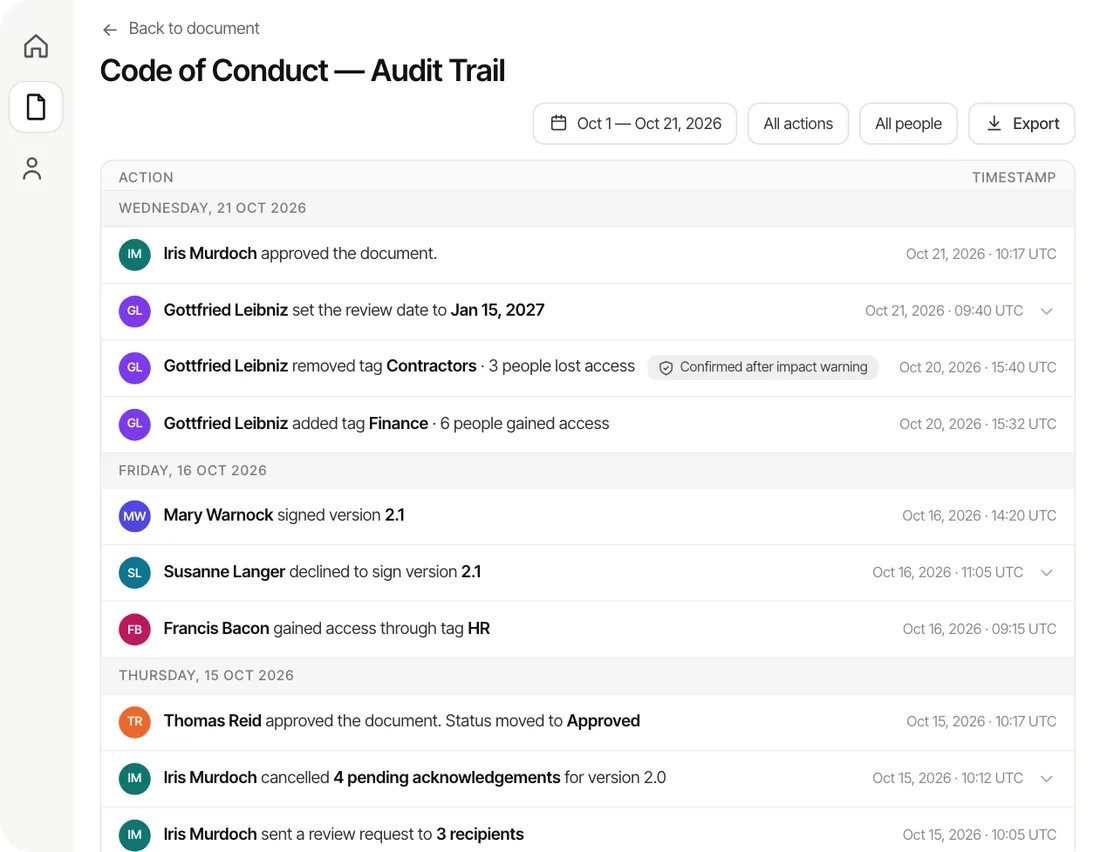
Filter the record by date, person or policy and export a PDF or CSV.
Each team gets its own policies
Tag people by team and location. Each policy reaches only the people it covers, and new hires get theirs on day one.
Policies by team
Information Security PolicyAll staff163 of 164 acknowledged
Acceptable Use PolicyAll staff164 of 164 acknowledged
Secure Development PolicyEngineering41 of 41 acknowledged
Incident Response PlanOps12 of 12 acknowledged
HAHannah ArendtNew engineer · Engineering tag
Information Security Policy: receivedInformation Security Policy: acknowledgedSecure Development Policy: receivedSecure Development Policy: acknowledged
Each team sees only the policies that cover it.
A new hire gets their team’s policies on day one.
A record for every employee
Show the auditor who has acknowledged which version, with the time and the statement they agreed to.
No. They read, acknowledge and sign as viewers, free of charge.
Acknowledgment or signature?
Both are available. Choose for each policy when you send it. e-sign is an add-on on the Scale plan.
What happens when a policy changes?
The new version is approved, then sent to everyone it applies to, who are asked again.
Can an auditor see a document without an account?
Yes. Add them as a one-time viewer and they open that document with a one-time code.
Does everyone have to acknowledge again every year?
Only when a policy changes or expires. If nothing changed at review, the date moves and no one is asked again. Where a standard expects a yearly acknowledgment, set the policy to expire each year and re-approve it.
Can IT keep its policies separate from other departments?
Yes. Each department edits its own policies, and tags decide who reads them.