Your security policies, approved and acknowledged, before the customer review.
For software and services companies certifying to ISO 27001 or ISO 42001, or answering customer security questionnaires. The policy set approved, sent to the people it covers, and on record by version.
Invite a new starter with their tags and their policies are waiting.
No seat cost for readers
Employees and other viewers are unlimited and free. You pay for the people who write.
Every change goes out again
A revised policy is approved, then everyone it covers is asked again, automatically.
Public where you want it
Publish chosen policies on your own domain, from the approved version.
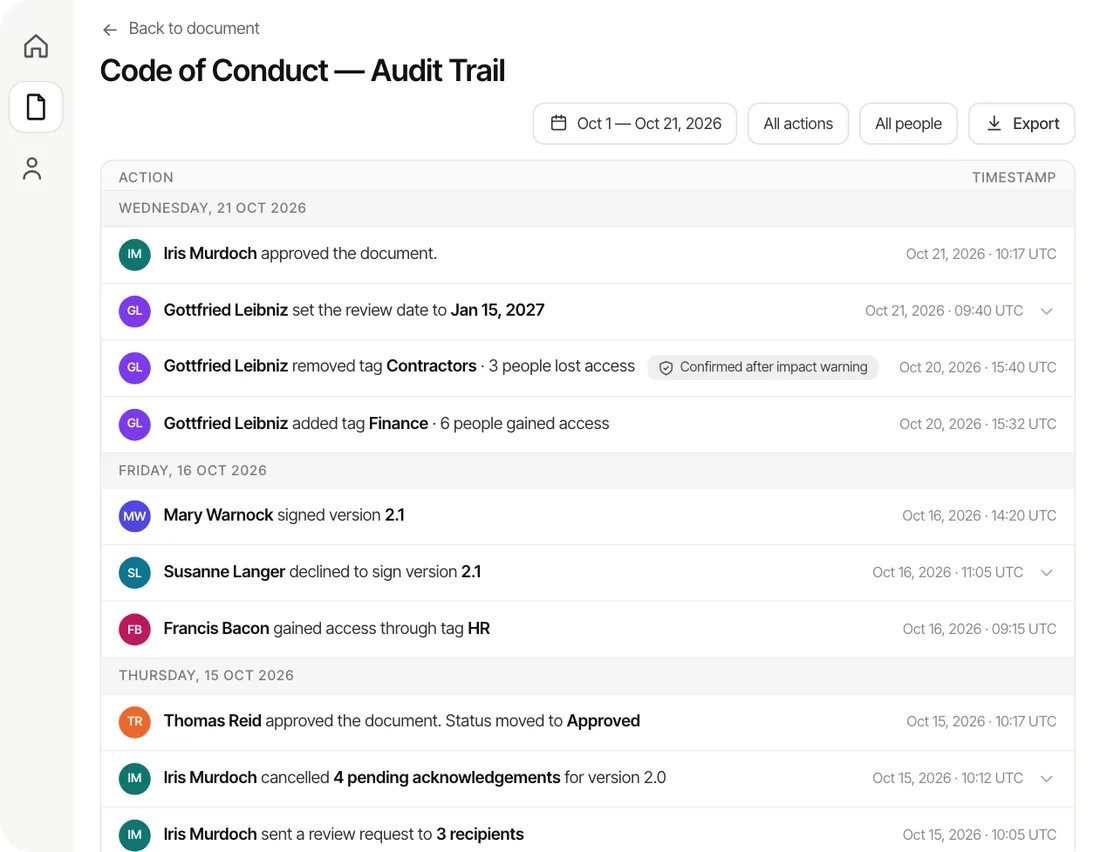
Proof on request
Filter the record by date, person or policy and export a PDF or CSV.
Each team gets its own policies
Tag people by team and location. Each policy reaches only the people it covers, and new hires get theirs on day one.
Policies by team
Information Security PolicyAll staff96 of 96 acknowledged
Secure Development PolicyEngineering41 of 41 acknowledged
Incident Response PlanOps12 of 12 acknowledged
AI Use PolicyAll staff96 of 96 acknowledged
HAHannah ArendtNew engineer · Engineering tag
Information Security Policy: receivedInformation Security Policy: acknowledgedSecure Development Policy: receivedSecure Development Policy: acknowledged
Each team sees only the policies that cover it.
A new hire gets their team’s policies on day one.
A record for every employee
Show the auditor who has acknowledged which version, with the time and the statement they agreed to.