See for yourself in the live sandbox. No login or signup.

Walk into the audit with the proof already gathered

The audit becomes a two-week scramble because the proof was never gathered in one place

Manual control mapping

Every audit starts by mapping policies to requirements from scratch.

Sign-offs untraceable

Finding who signed which version means chasing people and old inboxes.

Evidence in five systems

Drive, email, the HR tool, the ticket queue, someone's laptop.

And again next year

None of the work carries forward. The next audit starts from zero.

The Evidence Assembles Itself As You Work

No manual upkeep

Approvals and acknowledgments live with the policy, so the proof is already assembled when you need it. Nothing depends on someone keeping a spreadsheet current.

Export on demand

Produce a tamper-evident PDF for one document or CSV across the set the moment someone asks, with identities, timestamps, versions, and the attestation text people saw.

The version in force, on any date

When the question is "what did the policy say when it happened?", pull the version that was in force on that date, with its acknowledgments attached.

Standards And Controls Mapping

Bring the standard you answer to, map each policy to the requirements it satisfies, and see coverage at a glance, with the matrix exportable for the auditor. In build now.

We'll email you the day it ships.

The proof is gathered as you go

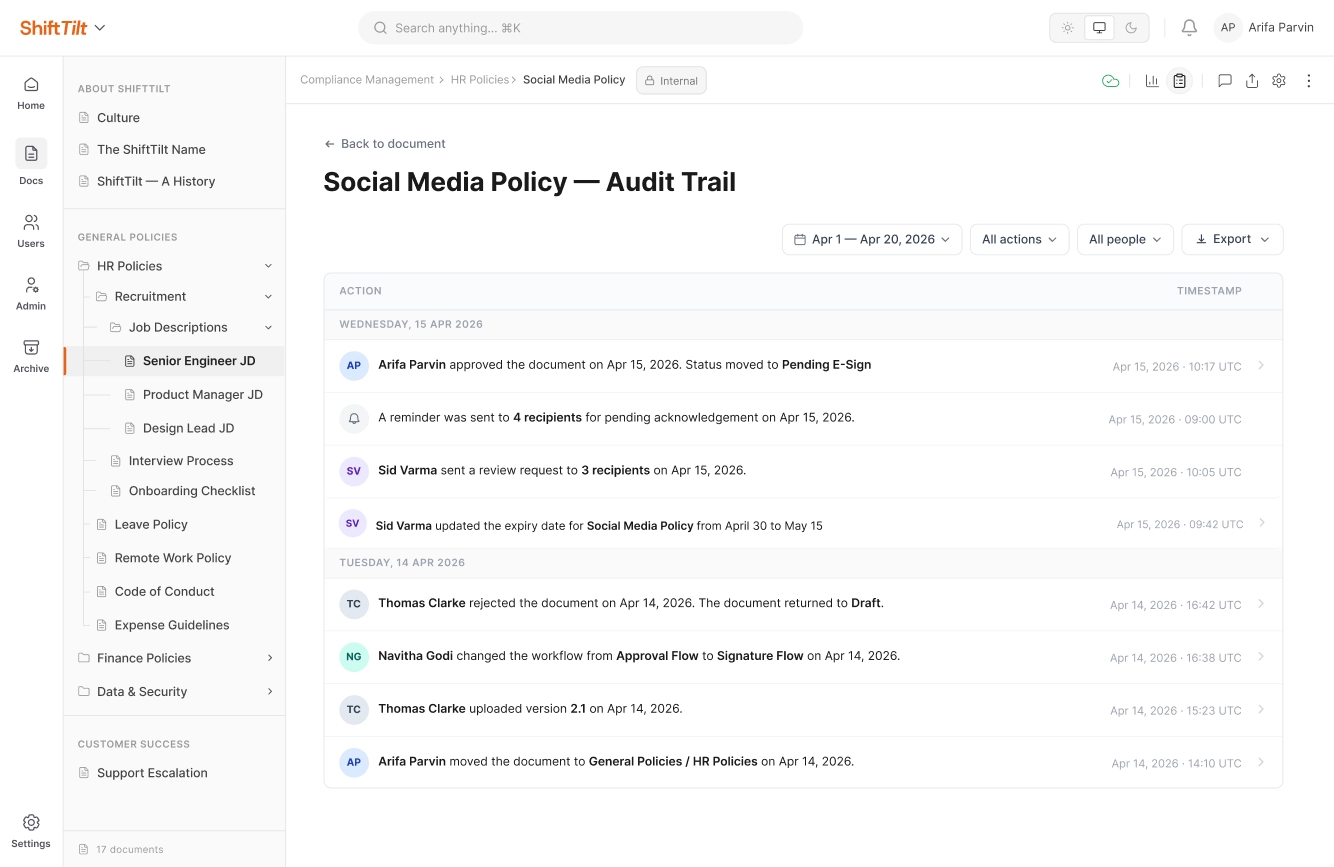
A per-document log of who saw, approved, and acknowledged each version - held with the policy itself, not assembled after the request comes in.

01

Per-document log

Who saw, approved, and acknowledged each version, in sequence.

02

Tamper-evident PDF

One document's complete record, in the form an auditor receives it.

03

CSV across the set

The whole policy set exported at once, scoped to what was asked for.

04

Attestation text on record

The exact statement each person saw, stored on their record.

05

Survives turnover

Completed records stay intact after someone leaves the company.

06

Coverage matrix

Requirement-by-requirement coverage, arriving with controls mapping.

For The Compliance Owner Facing SOC 2, ISO, HIPAA, Or A State Survey

The audit event changes; the layer you have to prove doesn't. Current policies, acknowledged versions, exportable records — whichever standard is on the letterhead.

USED FOR:

External audit

SOC 2, ISO 27001, and the annual certification cycle.

Regulatory survey

HIPAA, state inspections, and unannounced visits.

Customer security review

The questionnaire that lands mid-deal and holds it up.

Internal review

Board and internal-audit checks between the external ones.

Frequently asked questions

Do you provide the standards or the policy content?

No. You bring or author both; AllyMatter keeps the policies approved, acknowledged, and provable.

Yes. Export a complete, time-stamped record by version and audience, as tamper-evident PDF or CSV, with the attestation text each person saw.

That's what standards & controls mapping is for, and it's in build now. You'll bring your own standard, not just the common ones.

Be ready before the auditor asks

30-day free trial · No credit card · Cancel anytime

Scroll to Top