Your security program approved, acknowledged and ready to certify.

For insurers, agencies and brokers who answer to NY DFS, their state regulator and FinCEN. Cybersecurity, privacy and AML programs approved, sent to the people they cover, and on record by version.

30-day trialUnlimited free viewersNo credit card required

Five colleagues gathered around a laptop, one pointing at the screen while the others lean in and smile.

Ready for every certification

Strong agencies already have the program. The work is keeping the approvals, the training acknowledgments and every version as ready as the program.

23 NYCRR Part 500

NY DFS cybersecurity regulation

Policies approved every year by the senior governing body, staff trained, incident response and continuity plans kept, and the annual certification signed. For a small agency on the limited exemption, that is most of what is owed.

  • The yearly approval on a review date, with who approved
  • Each person’s acknowledgment by version
  • Plans and policies ready behind the certification

31 CFR 1025.210

Insurance AML program

Insurers with covered products keep a written AML program approved by senior management, and make it available to FinCEN on request.

  • The program approved, with senior management as approvers
  • Sent to the claims and sales teams it covers
  • Every version ready to share on request

NAIC Insurance Data Security Model Law

State insurance data security laws

States that adopted the model law expect a written information security program and a yearly report on it. One program can serve every state you write in.

  • One program, current, with its history
  • Reviews and approvals on record
  • Acknowledged by every employee it covers

How it helps an agency

Built for agencies and insurers who show policy control to regulators, carriers and partners.

The right policy to each team

Claims, sales and IT each get the policies that cover them.

New hires covered from day one

Invite a new producer with their tags and their policies are waiting.

No seat cost for staff

Producers and other viewers are unlimited and free. You pay for the people who write.

Yearly approvals on schedule

Review dates remind the policy owner ahead of the annual approval.

Every change goes out again

A revised policy is approved, then everyone it covers is asked again, automatically.

Proof on request

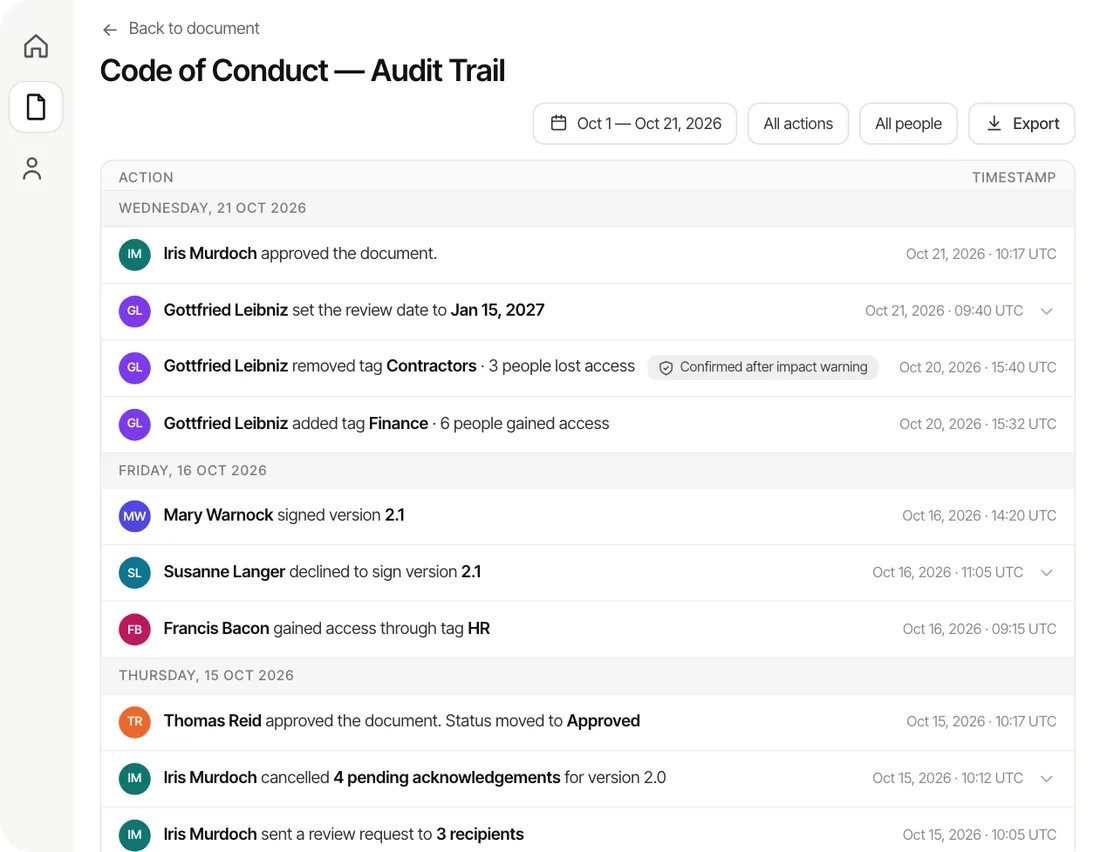
Filter the record by date, person or policy and export a PDF or CSV.

Each team gets its own policies

Tag people by office, team and line of business. Each policy reaches only the people it covers, and new hires get theirs on day one.

A record for every employee

Show the regulator who has acknowledged which version, with the time and the statement they agreed to.

The rest of the binder

Regulation covers part of it. An agency runs on many other policies, and they need the same control.

Privacy notice

One current version, published on your site if you choose, with its history kept.

Producer conduct

A code of conduct for producers and staff, current and acknowledged.

Vendor management

Third-party service provider procedures versioned and reviewed each year.

Claims handling procedures

Each adjuster on the current procedure, confirmed when it changes.

Harassment prevention

Staff in California and New York bring state policy and training duties with them.

Handbook and remote work

One current version for every employee, confirmed when it changes.

Ready for whoever asks.

Regulators, carriers and reinsurers ask the same thing in different words: the current program, who approved it and who has it.

Export the record as a PDF or CSV, or let an examiner open the document directly.

  • NY DFSAnnual policy approvals and training acknowledgments behind the certification
  • State regulatorsYour written information security program and its history
  • FinCENThe AML program, approved by senior management
  • Carriers and partnersYour security policies, approved and current

Built around your agency

Offices and linesTags such as Sales, Claims or Albany send each policy only to the people it covers.
Your boardAdd directors as approvers for the yearly approval of the cybersecurity policy.
ConsultantsBring in your security consultant as an external user to write and review.
ExaminersGive an examiner one document with a one-time code.

Need help writing the policies? Find a consultant for your standard.

Questions

Do producers and staff need a paid seat?

No. They read, acknowledge and sign as viewers, free of charge.

Acknowledgment or signature?

Both are available. Choose for each policy when you send it. e-sign is an add-on on the Scale plan.

What happens when a policy changes?

The new version is approved, then sent to everyone it applies to, who are asked again.

Can an auditor see a document without an account?

Yes. Add them as a one-time viewer and they open that document with a one-time code.

Can our board approve the cybersecurity policy here?

Yes. Add directors as approvers. Each approval is logged with the person and the time.

What happens to someone’s record when they leave?

Their completed acknowledgments stay on record.

Try AllyMatter free for 30 days

  • No credit card needed
  • 30-day money-back guarantee
  • Free migration on yearly plans